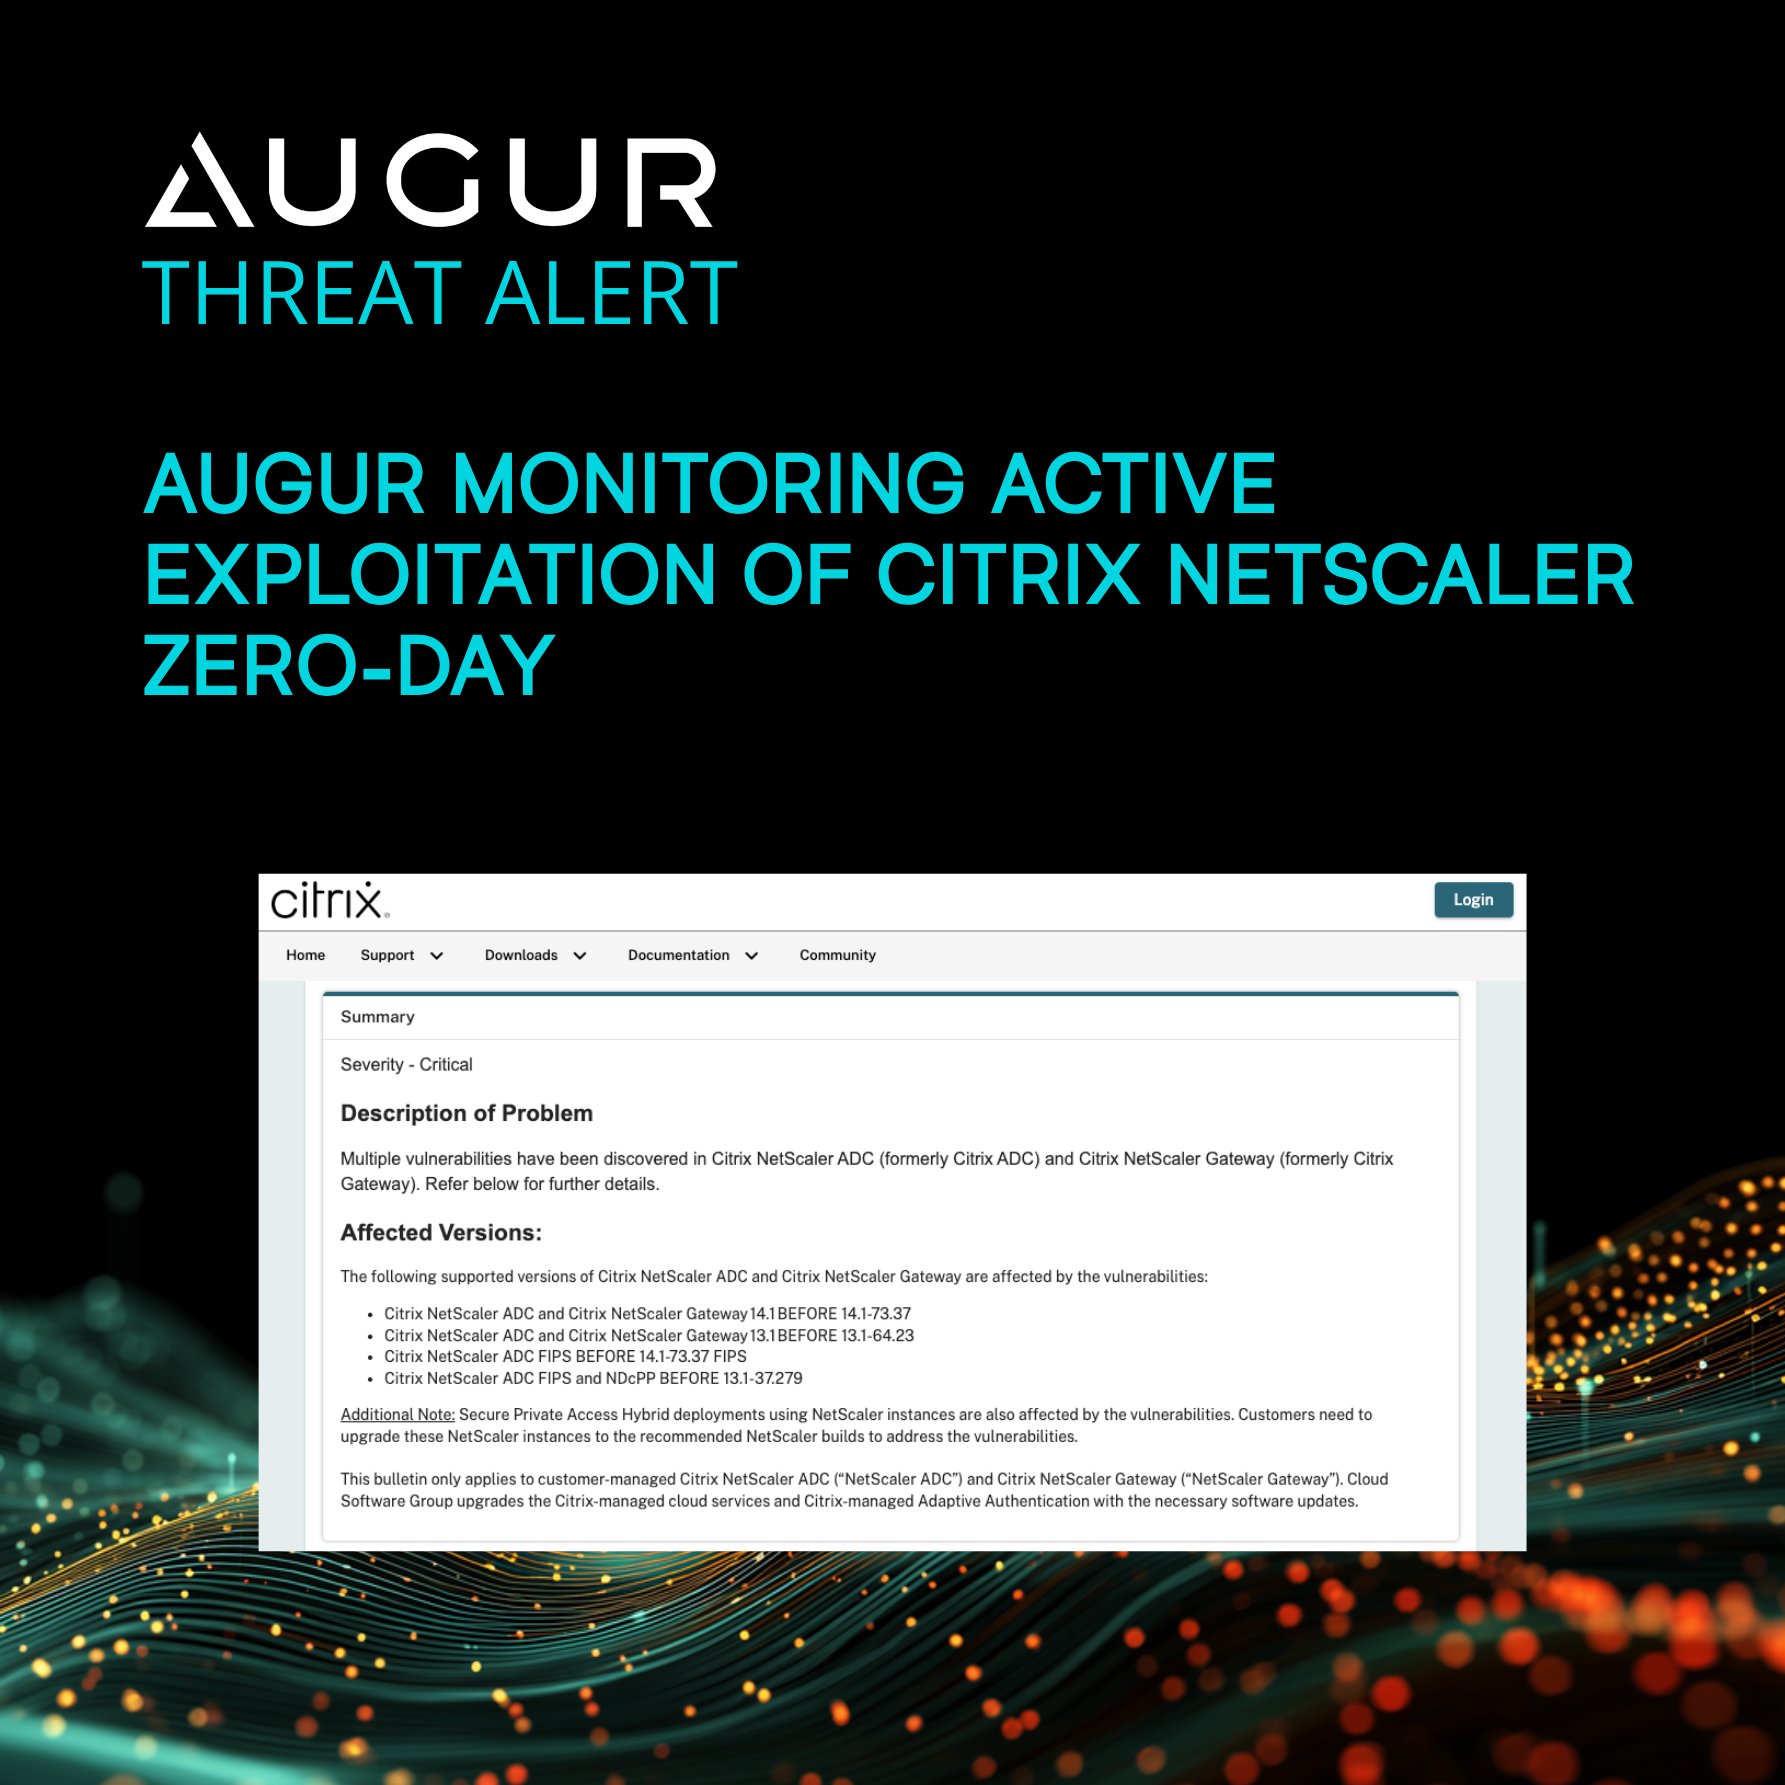
Citrix has confirmed active, in-the-wild exploitation of two critical zero-day vulnerabilities in customer-managed NetScaler ADC and NetScaler Gateway. CVE-2026-88771 and CVE-2026-88772 both carry a CVSS v4 score of 9.5, and both allow remote code execution. CVE-2026-88771 does not require authentication or an additional feature to be enabled on affected builds, which means appliances in their default configuration are exposed. CISA added both to its Known Exploited Vulnerabilities catalog on September 27, 2026.
The exposure is broad. These appliances sit at the network edge, handling VPN, remote access, and authentication, and Citrix says that every NetScaler ADC and NetScaler Gateway deployment is affected by at least one of the eight flaws in the bulletin. Fixed builds (14.1-73.37 and 13.1-64.23, plus FIPS editions) are available now. Organizations should upgrade immediately and check for signs of prior compromise, since patching alone does not evict an attacker who already has access.
What Augur is Doing
We strongly suspect we already have predictive coverage of the infrastructure tied to this activity. Our research team is in the process of confirming that now.
In parallel, we’re working directly with our clients to mitigate the impact.
More to come soon.
For the full vulnerability details from Citrix: https://support.citrix.com/support-home/kbsearch/article?articleNumber=CTX697096