
By the time a nation-state campaign is named, its infrastructure is usually old news. The servers were registered months, sometimes years, earlier. The command-and-control nodes were live long before any feed flagged them. That gap, the time between setup and use, has been all but invisible to threat researchers.
What if you could track that infrastructure before it’s weaponized, understand its lifecycle, and map its connections to see where the next threat will come from?
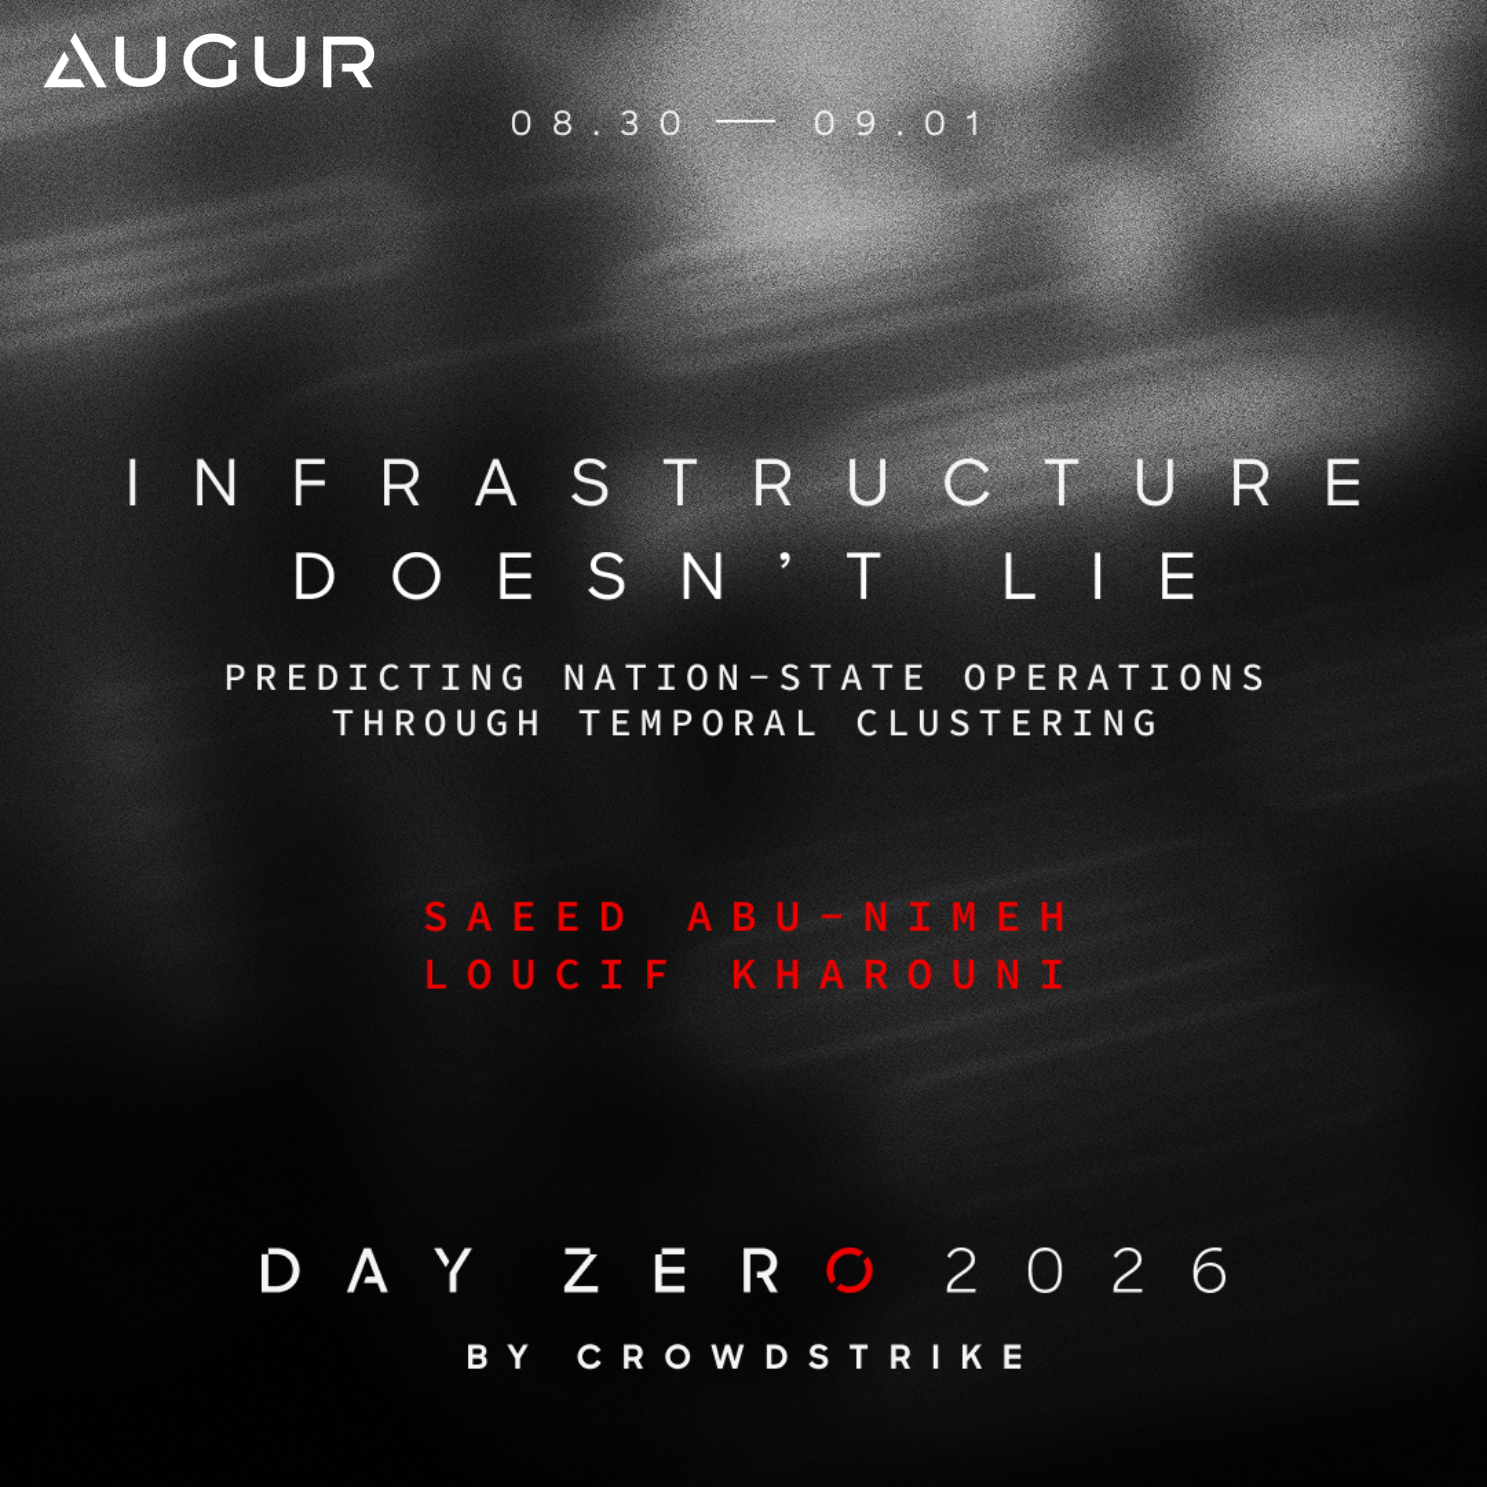
That’s the subject of new research from Augur, being presented by Founder and CTO Saeed Abu-Nimeh and SVP of Threat Research and Product Loucif Kharouni at Day Zero. The talk, titled "Infrastructure Doesn't Lie: Predicting Nation-State Operations Through Behavioral CIDR Clustering over Time," walks attendees through the research that demonstrates attack infrastructure follows a measurable lifecycle you can identify and act on while the intrusion is still preventable.
Making Infrastructure Patterns Visible
The evidence comes from Augur's predictive threat intelligence and its knowledge base of internet registration data spanning more than a decade. Using Augur’s investigative tools, that history can be leveraged to make the patterns visible. One tracked Russian cluster was flagged years before SolarWinds, ArcaneDoor, and a string of later CVEs traced back to the same CIDRs. The research walks through Russian, Chinese, and Iranian case studies where the infrastructure was visible long before disclosure.
It also shows the platform's investigative capabilities at work: pivoting across shared bulletproof hosting nodes to reveal how actors from three countries operate off the same abuse-tolerant infrastructure. And, in this case, a single block at that layer could have disrupted all of them.
If your team is still chasing named indicators, this is the research to watch
Saeed and Loucif are presenting "Infrastructure Doesn't Lie" at Day Zero, CrowdStrike's invite-only Threat Research Summit, on Monday, August 31 at 3:00 PM at Virgin Hotel, Las Vegas. Details are on the Day Zero agenda.
Attending the summit? Come find us.
And, if you want to meet with the Augur team for a closer look at what Preemptive Cybersecurity can contribute to your cyber defence, you can book a one-on-one here.